-
GAO seeks extra input on tech modernization contract
Prospective vendors will have just over an extra week to submit insights on GAO’s planned IT acquisition.
-
Congressman calls out State Department on senior staff abuses
Despite receiving multiple hostile environment complaints, the State Department reportedly did not discipline a Senior Executive Service employee.
-
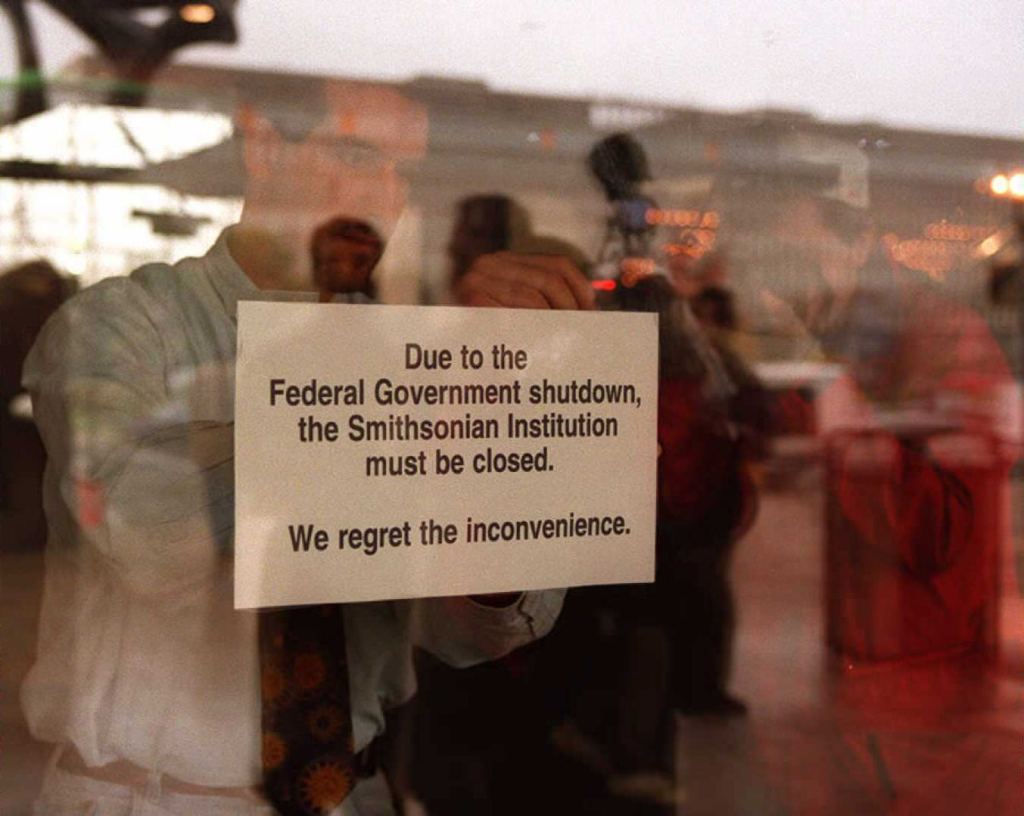
Employee groups slam playing politics with feds’ jobs
AFGE and NARFE officials said that even a short shutdown can have negative impacts on the federal workforce.
-
#schumershutdown trending with Russia-linked Twitter bots
Russian Twitter bots spent the weekend trying to blame Democrats for the government shutdown.
-
Contractors face greater uncertainty as shutdown looms
Much like federal employees, government contractors risk furlough, forced leave or shifting projects during a government shutdown.
-
One year on, vacancies plague Trump administration
Just prior to his one-year inauguration anniversary, Trump still leaves more key positions vacant than filled.
-
Congressional budget skirmishes won’t pause cyber issues
Worries that the government may shut down Friday at midnight have dominated the airwaves, but federal cyber policies and posture have seen a lot of activity in the past week. Here’s a roundup of the biggest stories.
-
Shutdown watch: Congress moves to put feds back to work
President Trump signed a bill Jan. 22 to fund the government through Feb. 8, 2018, ending the government shutdown that began at midnight on Friday, Jan. 19, 2018.
-
Shutdown could make it harder to prevent cyberattacks
Prolonged budget debates in Congress can inhibit federal agencies’ ability to effectively implement phases of the DHS Continuous Diagnostics and Mitigation program, which helps monitor and protect government networks.
-
Nearly half of federal agencies miss DHS email security deadline
The day after a Department of Homeland Security deadline for all federal agencies to implement a basic policy to protect email servers against malicious messages, just over half have actually done so, leaving the remainder still vulnerable.
-
GAO seeks extra input on tech modernization contract
Prospective vendors will have just over an extra week to submit insights on GAO’s planned IT acquisition.
-
Congressman calls out State Department on senior staff abuses
Despite receiving multiple hostile environment complaints, the State Department reportedly did not discipline a Senior Executive Service employee.
-
Employee groups slam playing politics with feds’ jobs
AFGE and NARFE officials said that even a short shutdown can have negative impacts on the federal workforce.
-
#schumershutdown trending with Russia-linked Twitter bots
Russian Twitter bots spent the weekend trying to blame Democrats for the government shutdown.
-
Contractors face greater uncertainty as shutdown looms
Much like federal employees, government contractors risk furlough, forced leave or shifting projects during a government shutdown.
-
One year on, vacancies plague Trump administration
Just prior to his one-year inauguration anniversary, Trump still leaves more key positions vacant than filled.
-
Congressional budget skirmishes won’t pause cyber issues
Worries that the government may shut down Friday at midnight have dominated the airwaves, but federal cyber policies and posture have seen a lot of activity in the past week. Here’s a roundup of the biggest stories.
-
Shutdown watch: Congress moves to put feds back to work
President Trump signed a bill Jan. 22 to fund the government through Feb. 8, 2018, ending the government shutdown that began at midnight on Friday, Jan. 19, 2018.
-
Shutdown could make it harder to prevent cyberattacks
Prolonged budget debates in Congress can inhibit federal agencies’ ability to effectively implement phases of the DHS Continuous Diagnostics and Mitigation program, which helps monitor and protect government networks.
-
Nearly half of federal agencies miss DHS email security deadline
The day after a Department of Homeland Security deadline for all federal agencies to implement a basic policy to protect email servers against malicious messages, just over half have actually done so, leaving the remainder still vulnerable.
-
GAO seeks extra input on tech modernization contract
Prospective vendors will have just over an extra week to submit insights on GAO’s planned IT acquisition.
-
Congressman calls out State Department on senior staff abuses
Despite receiving multiple hostile environment complaints, the State Department reportedly did not discipline a Senior Executive Service employee.
-
Employee groups slam playing politics with feds’ jobs
AFGE and NARFE officials said that even a short shutdown can have negative impacts on the federal workforce.
-
#schumershutdown trending with Russia-linked Twitter bots
Russian Twitter bots spent the weekend trying to blame Democrats for the government shutdown.
-
Contractors face greater uncertainty as shutdown looms
Much like federal employees, government contractors risk furlough, forced leave or shifting projects during a government shutdown.
-
One year on, vacancies plague Trump administration
Just prior to his one-year inauguration anniversary, Trump still leaves more key positions vacant than filled.
-
Congressional budget skirmishes won’t pause cyber issues
Worries that the government may shut down Friday at midnight have dominated the airwaves, but federal cyber policies and posture have seen a lot of activity in the past week. Here’s a roundup of the biggest stories.
-
Shutdown watch: Congress moves to put feds back to work
President Trump signed a bill Jan. 22 to fund the government through Feb. 8, 2018, ending the government shutdown that began at midnight on Friday, Jan. 19, 2018.
-
Shutdown could make it harder to prevent cyberattacks
Prolonged budget debates in Congress can inhibit federal agencies’ ability to effectively implement phases of the DHS Continuous Diagnostics and Mitigation program, which helps monitor and protect government networks.
-
Nearly half of federal agencies miss DHS email security deadline
The day after a Department of Homeland Security deadline for all federal agencies to implement a basic policy to protect email servers against malicious messages, just over half have actually done so, leaving the remainder still vulnerable.