-
IG: Poor firewall maintenance leaves USPS exposed
An auditor’s report shows USPS has neglected its firewalls, leaving the agency’s mail systems open to attacks.
-
OMB provides acting CIO for OPM
Deputy Federal CIO Lisa Schlosser is serving a detail at OPM as acting CIO while they find a full-time replacement.
-
NIH wants more veteran, HUBZone small businesses on GWAC
NITAAC is holding a ramp-on to add more small businesses to its CIO-SP3 acquisition vehicle.
-
Air Force Cyber Simulation Center preps to meet tighter deadlines
The Air Force brass want new tools from the Cyber Simulation Center a year earlier than first ordered, prompting the center to up its support contract.
-
NIST updates BYOD guidance for teleworking feds
Federal networks are vulnerable when employees use unsecured devices and networks but NIST has some advice.
-
FedRAMP seeking agile vendors to build public dashboard
The draft RFQ says FedRAMP will be looking for vendors currently on 18F’s Agile BPA.
-
10 ways HHS can shore up its cybersecurity
A new inspector general report details problems with Health and Human Services’ security posture and offers tips to bring it under compliance.
-
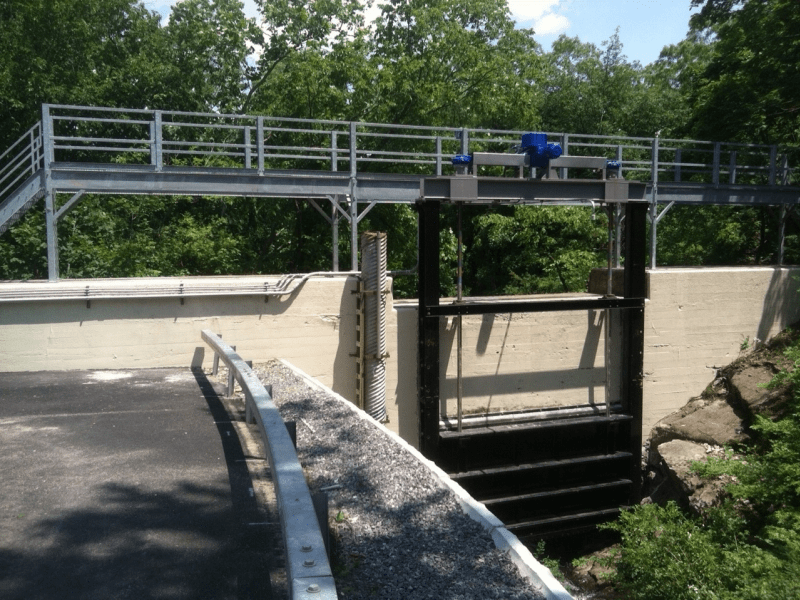
Report: Justice will indict Iranians connected to New York dam hack
The low-level hack occurred in 2013 but CNN reports an indictment is expected to drop next week.
-
Former Schedule 70 lead on who should fill her spot
GSA is looking for a new director for IT Schedule 70 and the former one has some ideas on what qualifications that person should have.
-
OMB moves to make all federal code open source
New draft policy will force agencies to share their code with each other and the public at large.
-
IG: Poor firewall maintenance leaves USPS exposed
An auditor’s report shows USPS has neglected its firewalls, leaving the agency’s mail systems open to attacks.
-
OMB provides acting CIO for OPM
Deputy Federal CIO Lisa Schlosser is serving a detail at OPM as acting CIO while they find a full-time replacement.
-
NIH wants more veteran, HUBZone small businesses on GWAC
NITAAC is holding a ramp-on to add more small businesses to its CIO-SP3 acquisition vehicle.
-
Air Force Cyber Simulation Center preps to meet tighter deadlines
The Air Force brass want new tools from the Cyber Simulation Center a year earlier than first ordered, prompting the center to up its support contract.
-
NIST updates BYOD guidance for teleworking feds
Federal networks are vulnerable when employees use unsecured devices and networks but NIST has some advice.
-
FedRAMP seeking agile vendors to build public dashboard
The draft RFQ says FedRAMP will be looking for vendors currently on 18F’s Agile BPA.
-
10 ways HHS can shore up its cybersecurity
A new inspector general report details problems with Health and Human Services’ security posture and offers tips to bring it under compliance.
-
Report: Justice will indict Iranians connected to New York dam hack
The low-level hack occurred in 2013 but CNN reports an indictment is expected to drop next week.
-
Former Schedule 70 lead on who should fill her spot
GSA is looking for a new director for IT Schedule 70 and the former one has some ideas on what qualifications that person should have.
-
OMB moves to make all federal code open source
New draft policy will force agencies to share their code with each other and the public at large.
-
IG: Poor firewall maintenance leaves USPS exposed
An auditor’s report shows USPS has neglected its firewalls, leaving the agency’s mail systems open to attacks.
-
OMB provides acting CIO for OPM
Deputy Federal CIO Lisa Schlosser is serving a detail at OPM as acting CIO while they find a full-time replacement.
-
NIH wants more veteran, HUBZone small businesses on GWAC
NITAAC is holding a ramp-on to add more small businesses to its CIO-SP3 acquisition vehicle.
-
Air Force Cyber Simulation Center preps to meet tighter deadlines
The Air Force brass want new tools from the Cyber Simulation Center a year earlier than first ordered, prompting the center to up its support contract.
-
NIST updates BYOD guidance for teleworking feds
Federal networks are vulnerable when employees use unsecured devices and networks but NIST has some advice.
-
FedRAMP seeking agile vendors to build public dashboard
The draft RFQ says FedRAMP will be looking for vendors currently on 18F’s Agile BPA.
-
10 ways HHS can shore up its cybersecurity
A new inspector general report details problems with Health and Human Services’ security posture and offers tips to bring it under compliance.
-
Report: Justice will indict Iranians connected to New York dam hack
The low-level hack occurred in 2013 but CNN reports an indictment is expected to drop next week.
-
Former Schedule 70 lead on who should fill her spot
GSA is looking for a new director for IT Schedule 70 and the former one has some ideas on what qualifications that person should have.
-
OMB moves to make all federal code open source
New draft policy will force agencies to share their code with each other and the public at large.