-
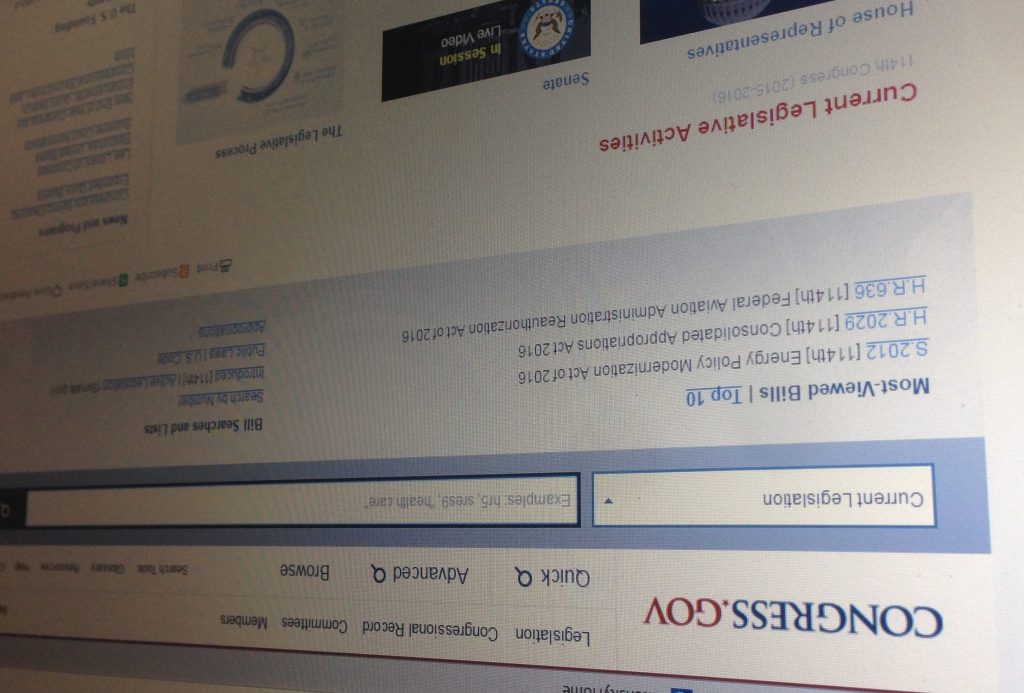
Thomas.gov set to retire this summer
The Library of Congress will officially make the switch from Thomas.gov to Congress.gov when the former site is turned off in July.
-
Congress investigating October FDIC data breach
The Committee on Science, Space and Technology asked for all documents related to the breach and subsequent internal discussions ahead of a formal briefing with FDIC officials.
-
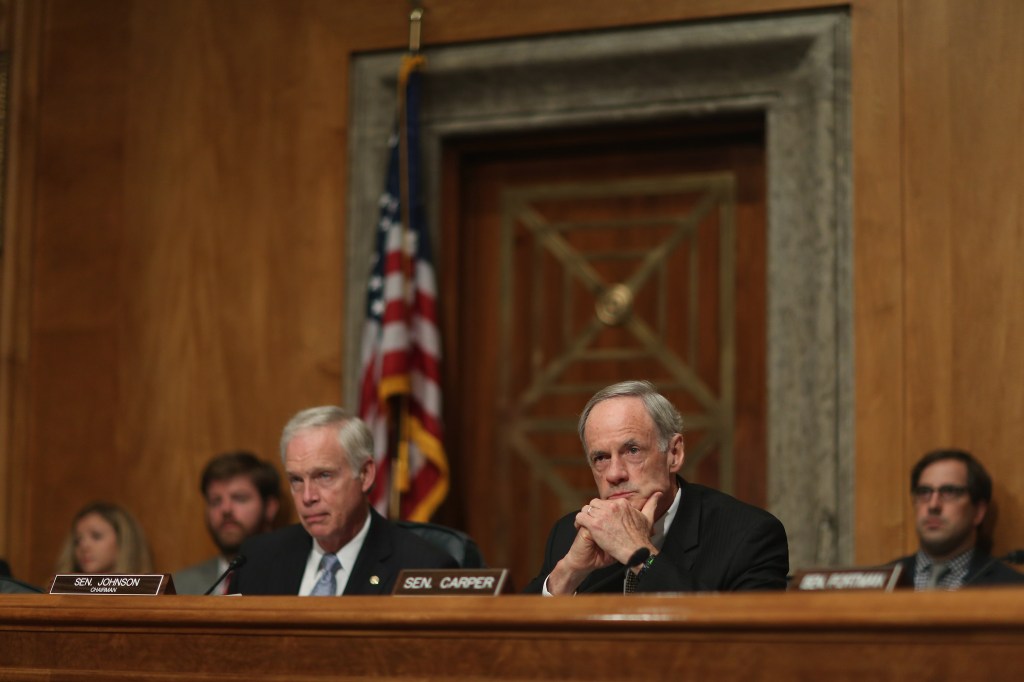
Senators want timeline on update to OMB’s main IT policy
Sens. Tom Carper, D-Del., and Ron Johnson, R-Wis., want to know exactly when OMB plans to issue its update to Circular A-130, the main IT management and cybersecurity guidance document.
-
Verizon breach report shows public, health sectors face similar threats
The public sector’s biggest threats come from misused credentials and miscellaneous errors.
-
OMB working on bimodal IT management policy
Federal CIO Tony Scott said the next big initiative will be about managing legacy and cutting-edge IT side-by-side.
-
GSA clears up confusion around Alliant 2 RFP
A new blog clarifies expected release of final RFPs and responds to contractors’ questions.
-
Retired fed spied on colleagues using manager’s login
Former Interior employee Dana Beach pleaded guilty in August to illegally accessing government networks after she retired.
-
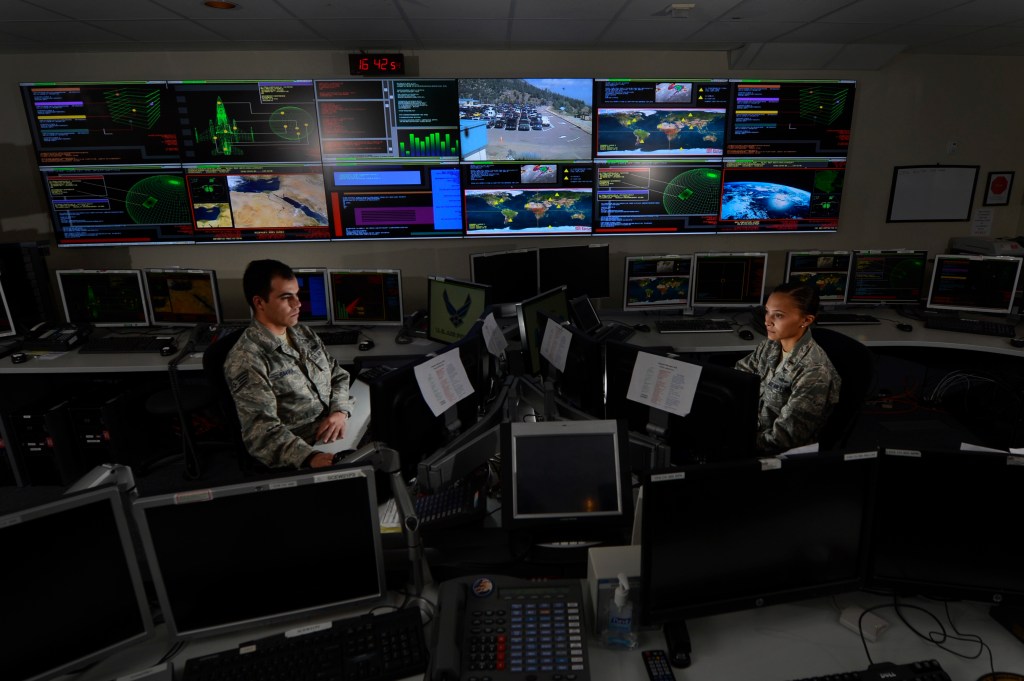
New Air Force policy sets roles for cyber offense, defense ops
A new directive from the secretary of the Air Force links cyber offense and defense, and sets out who is responsible for what.
-
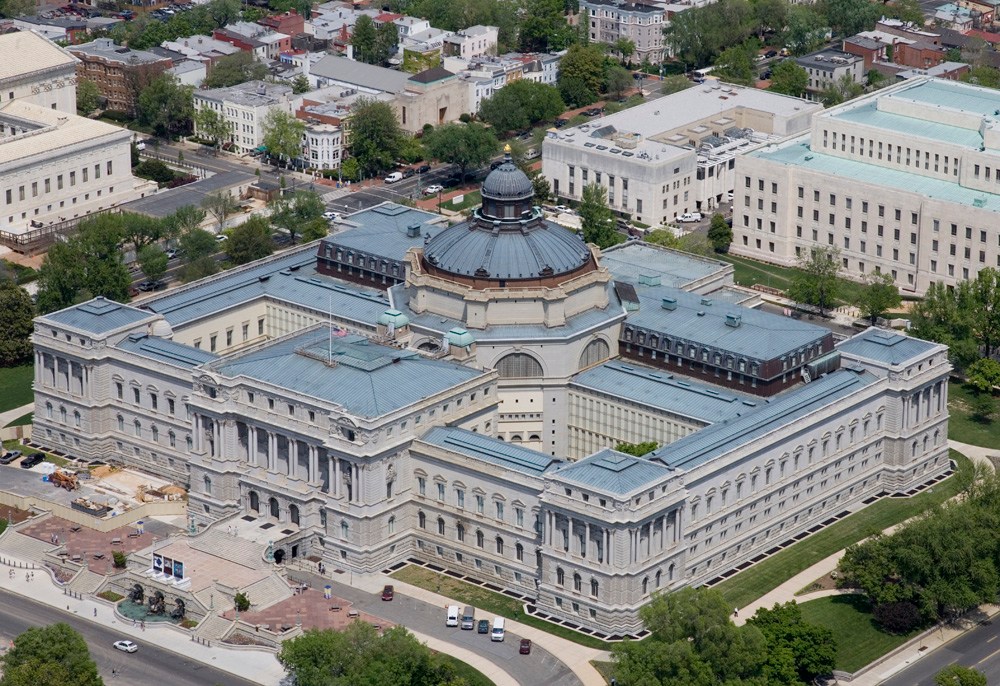
Library of Congress needs tech-savvy feds for speaker series
The Federal Library and Information Network’s IT working group put out a call for speakers for its brown bag series.
-
FDIC waited months to report major October data breach
According to an inspector general investigation, the FDIC CIO failed to report a significant cybersecurity incident for months after incorrectly labeling it a minor event.
-
Thomas.gov set to retire this summer
The Library of Congress will officially make the switch from Thomas.gov to Congress.gov when the former site is turned off in July.
-
Congress investigating October FDIC data breach
The Committee on Science, Space and Technology asked for all documents related to the breach and subsequent internal discussions ahead of a formal briefing with FDIC officials.
-
Senators want timeline on update to OMB’s main IT policy
Sens. Tom Carper, D-Del., and Ron Johnson, R-Wis., want to know exactly when OMB plans to issue its update to Circular A-130, the main IT management and cybersecurity guidance document.
-
Verizon breach report shows public, health sectors face similar threats
The public sector’s biggest threats come from misused credentials and miscellaneous errors.
-
OMB working on bimodal IT management policy
Federal CIO Tony Scott said the next big initiative will be about managing legacy and cutting-edge IT side-by-side.
-
GSA clears up confusion around Alliant 2 RFP
A new blog clarifies expected release of final RFPs and responds to contractors’ questions.
-
Retired fed spied on colleagues using manager’s login
Former Interior employee Dana Beach pleaded guilty in August to illegally accessing government networks after she retired.
-
New Air Force policy sets roles for cyber offense, defense ops
A new directive from the secretary of the Air Force links cyber offense and defense, and sets out who is responsible for what.
-
Library of Congress needs tech-savvy feds for speaker series
The Federal Library and Information Network’s IT working group put out a call for speakers for its brown bag series.
-
FDIC waited months to report major October data breach
According to an inspector general investigation, the FDIC CIO failed to report a significant cybersecurity incident for months after incorrectly labeling it a minor event.
-
Thomas.gov set to retire this summer
The Library of Congress will officially make the switch from Thomas.gov to Congress.gov when the former site is turned off in July.
-
Congress investigating October FDIC data breach
The Committee on Science, Space and Technology asked for all documents related to the breach and subsequent internal discussions ahead of a formal briefing with FDIC officials.
-
Senators want timeline on update to OMB’s main IT policy
Sens. Tom Carper, D-Del., and Ron Johnson, R-Wis., want to know exactly when OMB plans to issue its update to Circular A-130, the main IT management and cybersecurity guidance document.
-
Verizon breach report shows public, health sectors face similar threats
The public sector’s biggest threats come from misused credentials and miscellaneous errors.
-
OMB working on bimodal IT management policy
Federal CIO Tony Scott said the next big initiative will be about managing legacy and cutting-edge IT side-by-side.
-
GSA clears up confusion around Alliant 2 RFP
A new blog clarifies expected release of final RFPs and responds to contractors’ questions.
-
Retired fed spied on colleagues using manager’s login
Former Interior employee Dana Beach pleaded guilty in August to illegally accessing government networks after she retired.
-
New Air Force policy sets roles for cyber offense, defense ops
A new directive from the secretary of the Air Force links cyber offense and defense, and sets out who is responsible for what.
-
Library of Congress needs tech-savvy feds for speaker series
The Federal Library and Information Network’s IT working group put out a call for speakers for its brown bag series.
-
FDIC waited months to report major October data breach
According to an inspector general investigation, the FDIC CIO failed to report a significant cybersecurity incident for months after incorrectly labeling it a minor event.