-
Millennium Challenge seeks cyber training support
The foreign investment agency needs help training its employees on best practices around cybersecurity and privacy.
-
Committee slams FDIC CIO for ‘misleading’ testimony
A May 19 letter from the Committee on Science, Space and Technology offers FDIC leadership the opportunity to clarify “false and misleading” testimony about recent data breaches.
-
Second FITARA scorecard: Only one failing grade
A few agencies showed improvement but the majority received the same grade as the first scorecard in November.
-
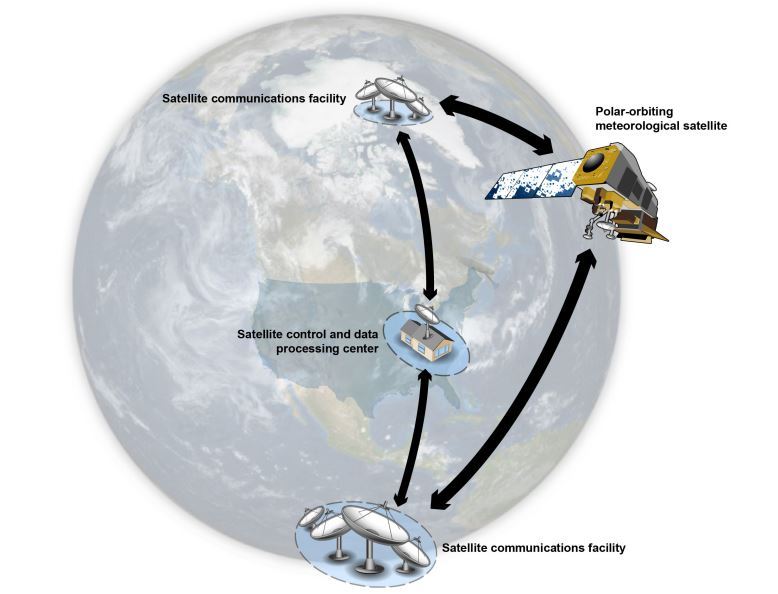
NOAA satellite gap solution suffers from infosec weaknesses
The agency is on track to mitigate the satellite data gap but its ground systems are vulnerable to cyberattacks and breaches.
-
Significant changes to final rule on fed data in contractor systems
New addition to the Federal Acquisition Regulation sets forth baseline controls for contractors safeguarding government data.
-
VA wants to scan dark web for stolen data
Navigating the Internet has become a routine thing since the invention of strong search engines like Google but not everything on the web is indexed and searchable.
-
18F moved too fast and something broke
Too much authorization for unauthorized apps left sensitive information on more than 100 employees exposed to the public for five months.
-
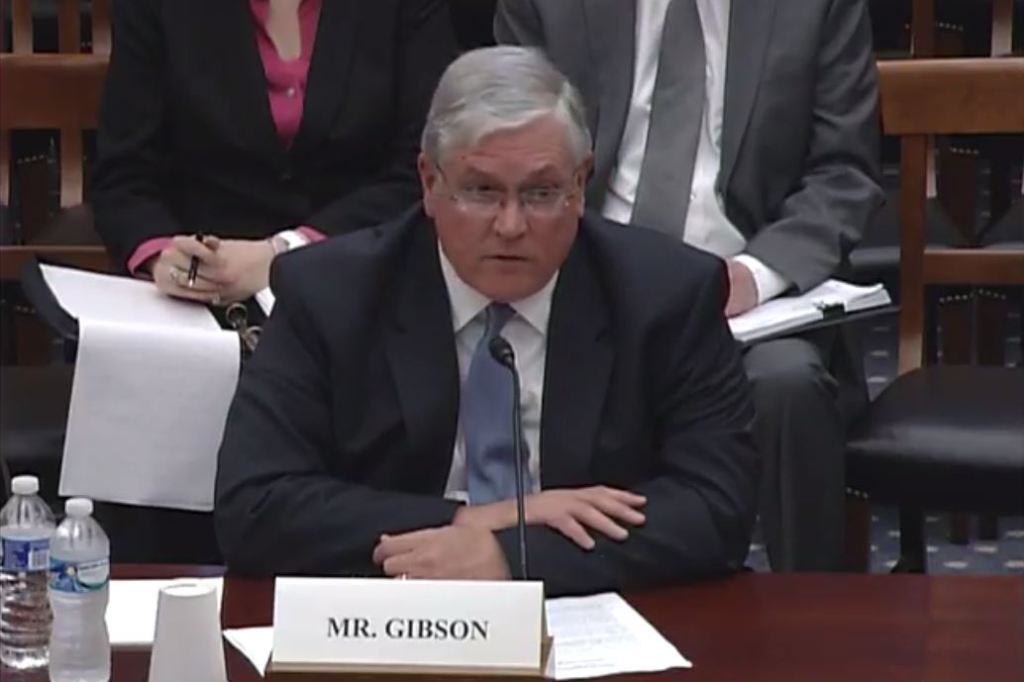
FDIC officials differ on what constitutes ‘major’ data breach
The FDIC CIO and acting inspector general explained to Congress why their definitions of “major” data breach don’t match up.
-
By what measure is an ISAO?
The information sharing standards organization released its first draft document, outlining what an ISAO should be and what guidance the group expects to release in the future.
-
Millennium Challenge seeks cyber training support
The foreign investment agency needs help training its employees on best practices around cybersecurity and privacy.
-
Committee slams FDIC CIO for ‘misleading’ testimony
A May 19 letter from the Committee on Science, Space and Technology offers FDIC leadership the opportunity to clarify “false and misleading” testimony about recent data breaches.
-
Second FITARA scorecard: Only one failing grade
A few agencies showed improvement but the majority received the same grade as the first scorecard in November.
-
NOAA satellite gap solution suffers from infosec weaknesses
The agency is on track to mitigate the satellite data gap but its ground systems are vulnerable to cyberattacks and breaches.
-
Significant changes to final rule on fed data in contractor systems
New addition to the Federal Acquisition Regulation sets forth baseline controls for contractors safeguarding government data.
-
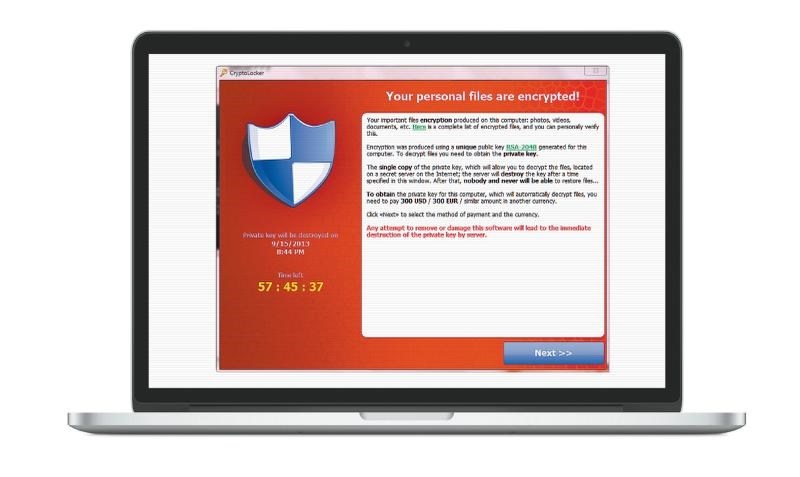
Beware the rise of ransomware
What agencies must do now to avoid cyber extortion.
-
VA wants to scan dark web for stolen data
Navigating the Internet has become a routine thing since the invention of strong search engines like Google but not everything on the web is indexed and searchable.
-
18F moved too fast and something broke
Too much authorization for unauthorized apps left sensitive information on more than 100 employees exposed to the public for five months.
-
FDIC officials differ on what constitutes ‘major’ data breach
The FDIC CIO and acting inspector general explained to Congress why their definitions of “major” data breach don’t match up.
-
By what measure is an ISAO?
The information sharing standards organization released its first draft document, outlining what an ISAO should be and what guidance the group expects to release in the future.
-
Millennium Challenge seeks cyber training support
The foreign investment agency needs help training its employees on best practices around cybersecurity and privacy.
-
Committee slams FDIC CIO for ‘misleading’ testimony
A May 19 letter from the Committee on Science, Space and Technology offers FDIC leadership the opportunity to clarify “false and misleading” testimony about recent data breaches.
-
Second FITARA scorecard: Only one failing grade
A few agencies showed improvement but the majority received the same grade as the first scorecard in November.
-
NOAA satellite gap solution suffers from infosec weaknesses
The agency is on track to mitigate the satellite data gap but its ground systems are vulnerable to cyberattacks and breaches.
-
Significant changes to final rule on fed data in contractor systems
New addition to the Federal Acquisition Regulation sets forth baseline controls for contractors safeguarding government data.
-
Beware the rise of ransomware
What agencies must do now to avoid cyber extortion.
-
VA wants to scan dark web for stolen data
Navigating the Internet has become a routine thing since the invention of strong search engines like Google but not everything on the web is indexed and searchable.
-
18F moved too fast and something broke
Too much authorization for unauthorized apps left sensitive information on more than 100 employees exposed to the public for five months.
-
FDIC officials differ on what constitutes ‘major’ data breach
The FDIC CIO and acting inspector general explained to Congress why their definitions of “major” data breach don’t match up.
-
By what measure is an ISAO?
The information sharing standards organization released its first draft document, outlining what an ISAO should be and what guidance the group expects to release in the future.